Compromised device swap.
A threat is detected, a clean device is collected and the old one is held with chain of custody.

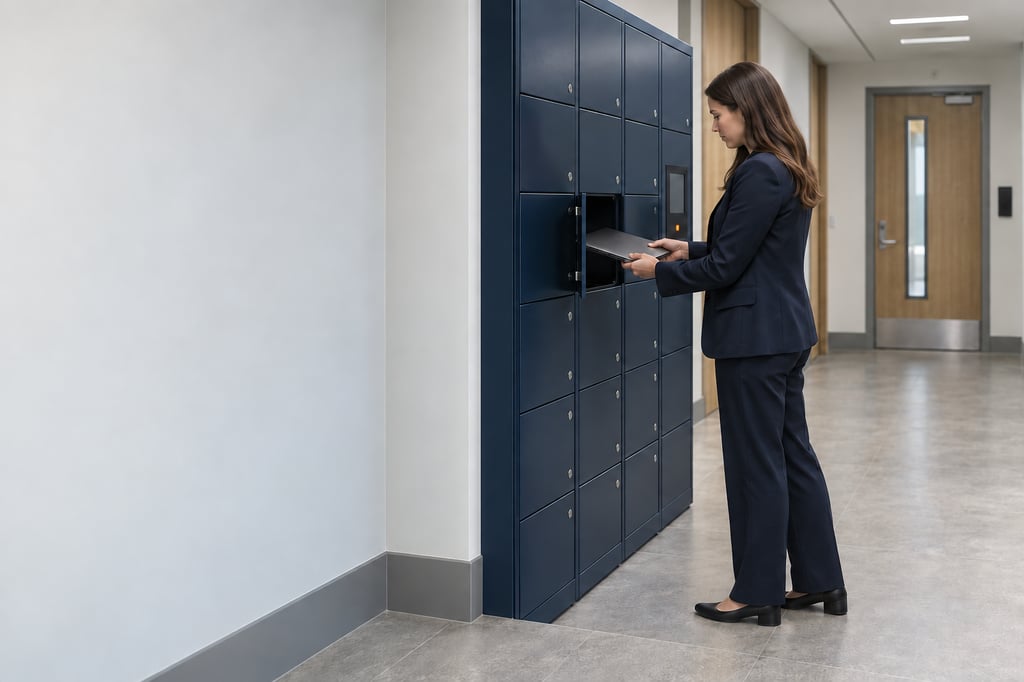
Tools you may already run, plus the one that hands the device over.
From the first signal to a device in hand.
CrowdStrike or Microsoft Defender detects a threat on a device.
ServiceNow SecOps isolates it through Intune and reserves a clean replacement.
The clean device is collected, and the suspect one is held in a locker for forensics.
The full sequence
- A threat is detected on a laptop.
- Security Incident Response opens an incident, and the host is isolated.
- The analyst decides the device must be replaced.
- Smart Collect® reserves a clean laptop and Intune assigns it to the user.
- The user collects the clean laptop and deposits the suspect one in the same cell.
- The suspect device is held in the locker until security collects it, with every access logged.
What you need in place
- CrowdStrike Falcon or Microsoft Defender for Endpoint
- ServiceNow Security Incident Response, with the vendor integration installed
- Microsoft Intune for wipe and reassignment
- Smart Lockers with clean spare devices
How the pieces connect
- CrowdStrike Falcon or Microsoft Defender
- Sends detections to ServiceNow Security Incident Response, and can isolate the host on request.
- ServiceNow SecOps
- Runs the security incident and decides on containment.
- Microsoft Intune
- Assigns the clean replacement, and wipes the suspect device when forensics allow.
- Smart Collect®
- Releases the clean device and holds the suspect one, with a chain of custody.
The physical steps stay the same, whichever system makes the decision.
Run this recipe from a standard ServiceNow workflow today, and let AI take the decision later. Nothing on the physical side changes.
One record of what was decided, and what physically happened.
A reference design for your technical team.
The Blueprint shows how this recipe would work in your ServiceNow instance and what a build would involve. It is a design, not a step-by-step installation guide.
- What you need in place. CrowdStrike Falcon or Microsoft Defender for Endpoint · ServiceNow Security Incident Response, with the vendor integration installed · Microsoft Intune for wipe and reassignment · Smart Lockers with clean spare devices
- How the pieces connect. The role of CrowdStrike Falcon, Microsoft Defender, ServiceNow SecOps and Microsoft Intune and Smart Collect®, and what stays in your instance
- Step by step. All 6 steps, from the first signal to the returned device
- Approval and policy. Only the security team can trigger a swap from a security incident.
- Handover rules and exceptions. Reservations, codes, expiry, returns, and what happens when stock runs out or nobody collects
- What to measure. Time from detection to clean device in hand · Time the suspect device spends outside custody · Analyst time per device swap
- What a build involves. The questions to settle first, the roles involved, and how we would scope a six to eight week pilot
Request the Blueprint
A four-page reference design for your technical team. Tell us who you are and the Blueprint downloads straight away.
Before you ask
Can anyone open the quarantine cell?
No. The cell is reserved for named security staff, and every open is recorded against the security incident.
Is this an off-the-shelf integration?
No. It is a recipe concept that shows what becomes possible when these tools are combined with Smart Collect®. We build it with you, and where needed with the vendor, when it fits your estate.
Where does the data live?
In your own ServiceNow instance. Smart Collect® does not keep a separate database of your users or devices.
Do we need AI for this?
No. A standard ServiceNow workflow can run every step today. Otto or Flow can take over the decision later without changing anything on the physical side.