Tracked Asset Handoff Guide for Enterprise IT Teams
A tracked asset handoff is a physical transfer of a device, from one custodian to another, that leaves a verifiable record: which asset, who released it, who received it, when, in what condition, and with what acknowledgement. Most enterprises can describe this on paper. Far fewer can prove it for every laptop swap, loan and return across every site. This guide sets out what a tracked handoff must capture, where custody chains typically break, and how to design the process so the record is produced by the handoff itself rather than reconstructed afterwards.
TL;DR
- A defensible handoff records five things: asset identifier, both custodians, timestamp, physical condition and acknowledgement of receipt.
- Chains of custody usually fail in the gap between release and receipt, not at either end. Scanning serial numbers at both ends closes it.
- The handoff should update the asset register as a transaction, not as a later clerical task.
- Where the handoff workflow runs inside the same ServiceNow tenant as the CMDB, RBAC and audit trail, there is nothing to synchronise and nothing extra to review.
- Treat a routine laptop swap with the rigour you would apply to a decommissioned drive, particularly in pharma, defence, legal and financial services.
Table of Contents
- What counts as a tracked handoff
- The five data points every handoff should capture
- Where custody chains actually break
- Designing the handoff as a transaction
- Treat the data on the device as part of the handoff
- Why the location of the workflow matters
- Perspective: what we see in physical handovers
- Applying the guide across use cases
- Measuring whether your handoffs are tracked
- How we help
- Common pitfalls to avoid
- FAQ
- Sources
What counts as a tracked handoff
The word “tracked” does the work here. A handoff that happens in a corridor and is logged in a spreadsheet on Friday afternoon is a handoff with a note attached. A tracked handoff is an event in the asset’s lifecycle, created at the moment custody changes, with the identity of both parties established by the system rather than typed in by hand.
That distinction matters to auditors. The evidence they look for is custodial continuity: an unbroken sequence of signatures, timestamps and state changes, as practitioner guidance on asset handover and return describes it. If any link is missing, the chain is a set of assertions rather than evidence.
The principle also sits comfortably within formal standards. ISO/IEC 19770-1 sets out requirements for an IT asset management system, and its practical premise is that asset decisions rely on trustworthy data. Physical movement is where that data most often goes stale. A device assigned to one person in the register and sitting on another person’s desk is the commonest form of the problem.
The five data points every handoff should capture
The research we draw on for this guide converges on five core data points for a robust handoff. The source is written for retired devices, but the same fields apply to every transfer in the lifecycle.
| Data point | What good looks like | Common failure |
|---|---|---|
| Asset identifier | Serial number or asset tag scanned, not typed | Transcription errors; tag and serial mismatch |
| Custodian identity | Releasing and receiving parties authenticated through corporate identity | Shared logins; names written on forms |
| Timestamp | System-generated at the moment of transfer | Back-filled after the event |
| Condition | Operational state and accessories recorded, ideally with evidence | “Good” as a free-text default |
| Acknowledgement | Receiver confirms receipt in the workflow | Verbal confirmation only |
The same source reports that standardising handover data helps asset registers reconcile discrepancies, with inventory inaccuracies typically falling by 20 to 30 per cent in large enterprises. Treat that as an indicative range rather than a promise: the improvement depends on how poor the starting register is.
Two refinements are worth making. First, authenticate the receiving custodian against your identity provider rather than relying on a name field. Second, make condition a structured choice with required accessories (charger, dock, security token) rather than a comment box. Structured fields can be reported on; comments cannot.
Where custody chains actually break
Practitioners consistently point to the same weak spot: the gap of uncertainty between shipping and receiving. A device leaves a stockroom, travels through a courier, a reception desk or an engineer’s bag, and arrives. For some hours or days, the register says one thing and reality another.
In enterprise IT support the pattern shows up in familiar scenarios:
- New-starter kit-out. The laptop is allocated to a joiner in the register, but is collected by a line manager, a colleague or an engineer. Nobody scans it at pick-up.
- Broken-device swap. The replacement is issued before the faulty unit is returned. For a time, two devices are assigned to one person, or the faulty one is unassigned and untraceable.
- Loans. Short-term loan devices leave with a verbal promise to return them, and the due date lives in someone’s calendar.
- Peripheral requests. Headsets and docks move in volume with almost no record, so consumption data and shrinkage are invisible.
- Returns at offboarding. Leavers return kit to a manager, a desk drawer or the post room, with no timestamp and no condition check.
Each of these relies on a person remembering to update a record. Each therefore depends on a person being available, at a site, during office hours. That is the structural reason physical handoffs resist the automation that has reached the digital layers of the service desk.
Designing the handoff as a transaction
The most useful reframing is to treat every handoff as a transaction that triggers an update in the asset register. The register should never need a separate reconciliation step because the handoff and the update are one act.
A seven-step pattern
- Request and approval. A ticket or catalogue request defines the entitlement: who is getting what, and why.
- Allocation. A specific asset, identified by serial number, is reserved against that request. The asset state moves accordingly.
- Release. The releasing custodian, whether a stockroom, an engineer or an automated point of collection, confirms the exact serial number leaving custody.
- In-transit state. If the device moves between locations, it holds a defined state such as pending transfer, so the register never claims it is somewhere it is not.
- Authenticated receipt. The receiving custodian identifies themselves and scans or confirms the serial number at the point of collection.
- Condition and accessories. Both are recorded in structured fields, with exceptions flagged for follow-up.
- Closure. The ticket closes only when the register reflects the new custodian, location and state.
ServiceNow’s own Hardware Asset Management documentation describes lifecycle states and stockroom tracking that map well to this pattern: assets move through states as they are received, assigned, repaired or retired, and the CMDB stays aligned. The design question is therefore not which states exist, but whether the physical event reliably causes the state change.
Authentication and access at the handoff point
Wherever devices are released without a person present, the handoff point becomes a control in its own right. Role-based access, authentication of the collector, tamper evidence, and a clear record of who can open what all need to be designed rather than assumed. Teams that run this as part of a broader physical security programme may find formal grounding in integrated security systems management training, which covers how access control, monitoring and governance fit together across a site.
Treat the data on the device as part of the handoff
A tracked handoff is about the information on the device as much as the device itself. NIST SP 800-88 Revision 1 is the reference guidance on media sanitisation, and its core idea is that confidentiality depends on managing information throughout the lifecycle, including its disposition. Although it focuses on sanitisation, its framework for hardware that holds data is a sound model for custody records generally: a documented history of location, status and authorised handler.
In practice, regulated organisations should apply it as follows:
- Treat a returned laptop as a data-bearing asset from the moment it leaves its user, whatever the reason for return.
- Record the intended disposition (redeploy, repair, sanitise, retire) at the time of the handoff, not later.
- Keep returned devices in a controlled state, with logged access, until the disposition is carried out.
- Retain the record in line with your own retention policy and the audit requirements of your sector, such as GxP in life sciences or the expectations of your regulator in financial services. Your compliance function should confirm the exact retention period.
This is also where the gap between digital and physical controls is most visible. The security policy that governs the data on a laptop is usually applied through the same ServiceNow estate that records the laptop. If the handoff record lives somewhere else, those two histories drift apart.
Why the location of the workflow matters
There are two broad ways to automate physical handoffs. One connects a separate application to ServiceNow through an API or middleware. The other runs the application natively inside the customer’s tenant.
From a platform owner’s perspective, the differences are concrete:
| Consideration | API-integrated approach | Tenant-native approach |
|---|---|---|
| Asset and audit data | Often replicated into a separate database | Held as native records in the CMDB |
| Access control | Separate roles to administer | Inherits the tenant’s RBAC |
| Security review | A fresh vendor review for the data flow | Existing tenant posture applies |
| Platform upgrades | Vendor may lag releases | Can track the release schedule |
| Reconciliation | Sync errors need monitoring | No sync to fail |
None of this makes an integrated approach unworkable, and many organisations run them successfully. But for custody records, the cost of two sources of truth is highest exactly when it is hardest to detect: during an audit, when the two histories disagree.
Perspective: what we see in physical handovers
We built Velocity Smart Collect® around a single observation. Digital service desk workflows now close most of a ticket automatically, and then stall at the point where someone has to hand over a device. The handoff is the last manual step, and it is also the step where audit evidence is weakest.

Our view is that the record should be a by-product of the handover, not a task attached to it. That is why Smart Collect runs inside the customer’s ServiceNow tenant. Asset state, device location and ownership history become native CMDB records that can be queried like any other configuration item, and the access model is the one the organisation already governs. We would rather a platform owner could answer “where is this data and who can see it?” with “in the tenant, as it always was” than with a data-flow diagram.
We also think the guide above applies whatever technology you choose. Start with the five data points, close the gap between release and receipt, and decide the disposition of the device at the time of handoff. The tooling then has a clear specification to meet.
— Anthony
Applying the guide across use cases
The same transaction pattern adapts to each handover type, with different emphasis.
New-starter kit
The priority is timing and identity. The device should be allocated before day one, and the new starter should be authenticated at collection, so that the record shows the right person took the right serial number at a known time. This removes the dependency on a manager or an engineer being at the desk on a Monday morning.
Break-fix swaps
The priority is pairing. Issue the replacement and receive the faulty device within one linked workflow, so the register never holds an unexplained gap. Record the condition of the faulty unit on return, since this supports warranty claims and data-handling decisions.
Loans and returns
The priority is due dates and escalation. A loan that is tracked from the start can chase itself. We have seen deployments report around 90 per cent of IT-staff time recovered on late returns, because reminders and escalations no longer rely on people.
Peripherals and consumables
The priority is low-friction recording. Items such as headsets, keyboards and cables are individually cheap, but in aggregate they generate a large share of low-value tickets. Self-service dispensing against an authenticated request gives both a record and consumption data.
Measuring whether your handoffs are tracked
A tracked handoff process should be testable. Four measures are usually enough to start:
- Register accuracy. Sample a set of devices at desks and compare them with the register. The mismatch rate is your baseline.
- Handoff completeness. The share of handoffs with all five data points captured automatically.
- Time in transit. How long assets sit in a pending state between release and receipt.
- Manual touch rate. How many handoffs still need an engineer to be present or to correct a record.
From our own deployments we have recorded outcomes such as 70,000+ transactions tracked, a 60 per cent reduction in on-site tickets and a 35 per cent reduction in IT-staff travel. These vary by estate, site count and use case, so treat them as indicative and baseline your own figures before a pilot.
How we help
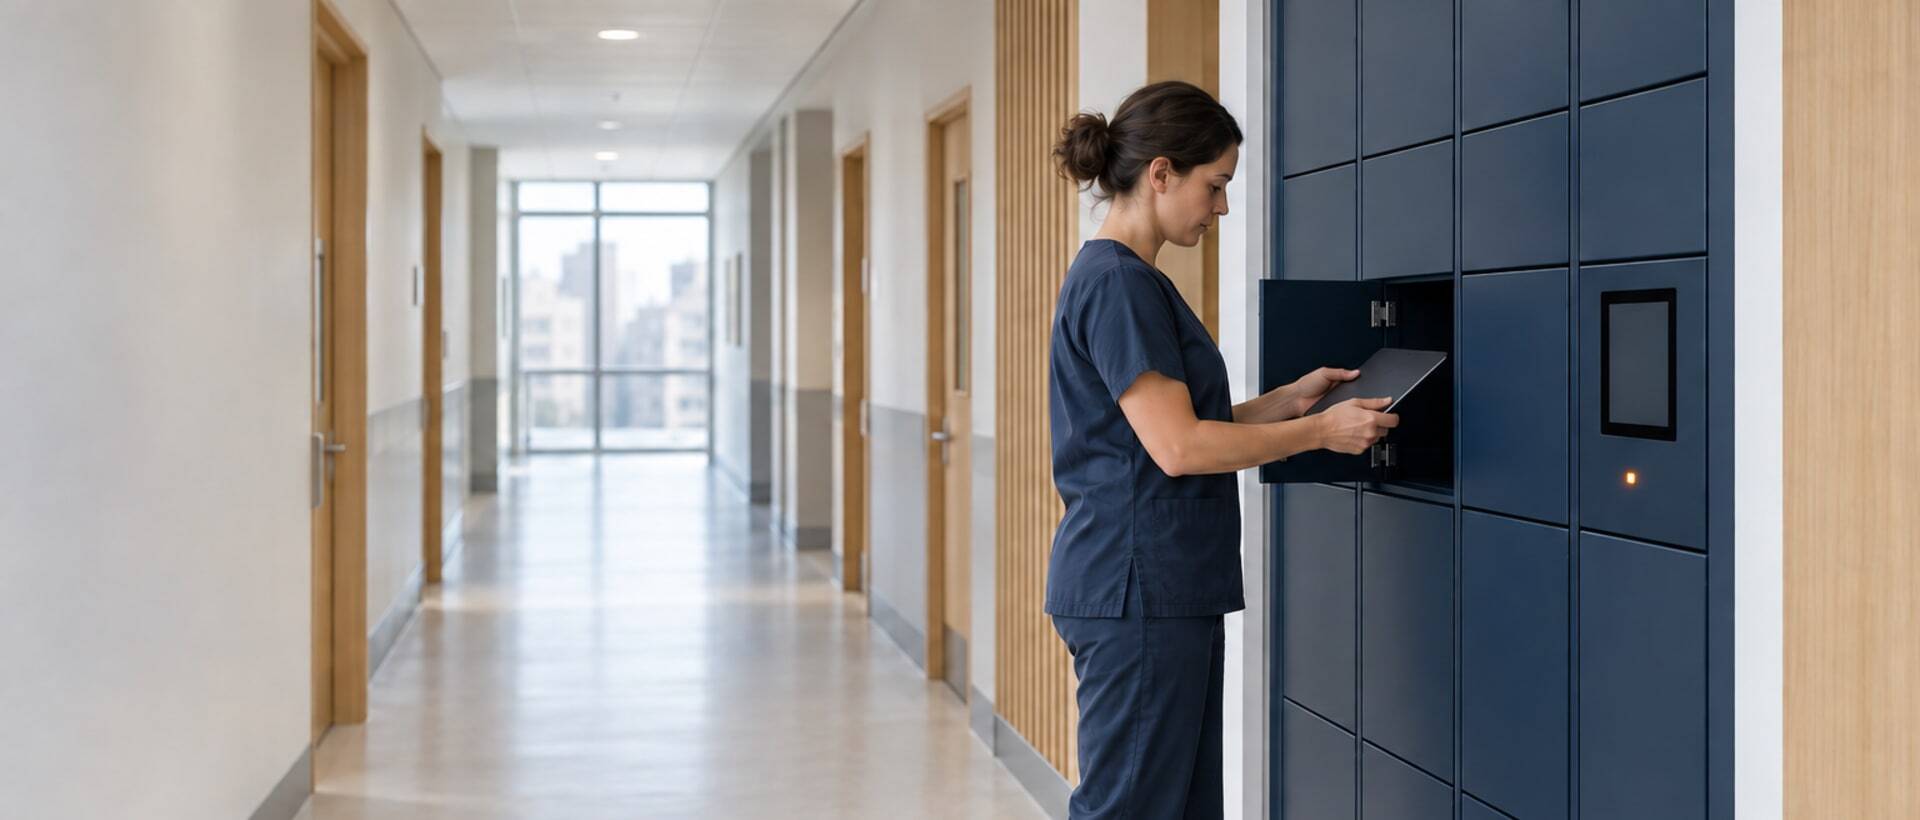
If you want to see the pattern run against your own entitlements and sites, Smart Collect® is the ServiceNow-native platform that orchestrates Smart Lockers for full-device handovers, Smart Vending for peripherals and Smart Kiosks for AI-assisted IT support. Our Use Case Validation and Live Pilot Programme let you test the handoff record against your own audit requirements before committing to a wider rollout.
Common pitfalls to avoid
- Automating the form, not the event. A digital form completed after the handover is still a retrospective record.
- Allowing shared or generic custodians. If “IT desk” is the custodian, nobody is.
- Leaving condition as free text. You cannot report on it, and it will not stand up as evidence.
- Ignoring the return leg. Many programmes track issue carefully and returns barely at all.
- Separating the data from the policy. A record held outside the tenant that governs the device invites drift.
FAQ
What is the difference between asset handover and asset handoff?
In IT asset management the terms are used interchangeably. Both describe the transfer of custody of a device between parties. “Tracked” adds the requirement that the transfer produces a verifiable record rather than relying on memory or a retrospective form.
What should a handoff record contain at minimum?
The asset identifier, the identity of the releasing and receiving custodians, a timestamp, the physical condition including accessories, and the receiver’s acknowledgement. Regulated organisations often add the intended disposition of the device and the ticket reference that authorised the movement.
How long should handoff records be kept?
That depends on your sector, your regulator and your internal retention policy, so confirm it with your compliance or legal function. As a rule, keep custody records for at least as long as you must evidence the device’s data handling, and make sure they remain queryable rather than archived out of reach.
Can a handoff be tracked without an engineer present?
Yes, provided the release point authenticates the collector, records the serial number at the moment of release, and writes the result to the asset register automatically. The control moves from a person’s attention to the system’s design, so the design needs to be reviewed with your security and audit teams.
Sources
- Asset Handover and Return Checklist Guide
- ITAD Chain of Custody: Enterprise Tracking Checklist
- ISO/IEC 19770-1:2017, IT asset management systems
- NIST SP 800-88 Revision 1, Guidelines for Media Sanitization
- Guidelines for Media Sanitization, NIST
- Mastering Hardware Asset Management in ServiceNow, ServiceNow Community
See what Smart Collect® could save you
Model your savings in two minutes, or book a 60-minute workshop to pressure-test the numbers against your estate.